The internet had its worst Wednesday ever. Then a master key turned out to be 4
One long list of disasters reached 3 million people in a day. We checked every line. Most of it is true, and the strangest part is the most solid.
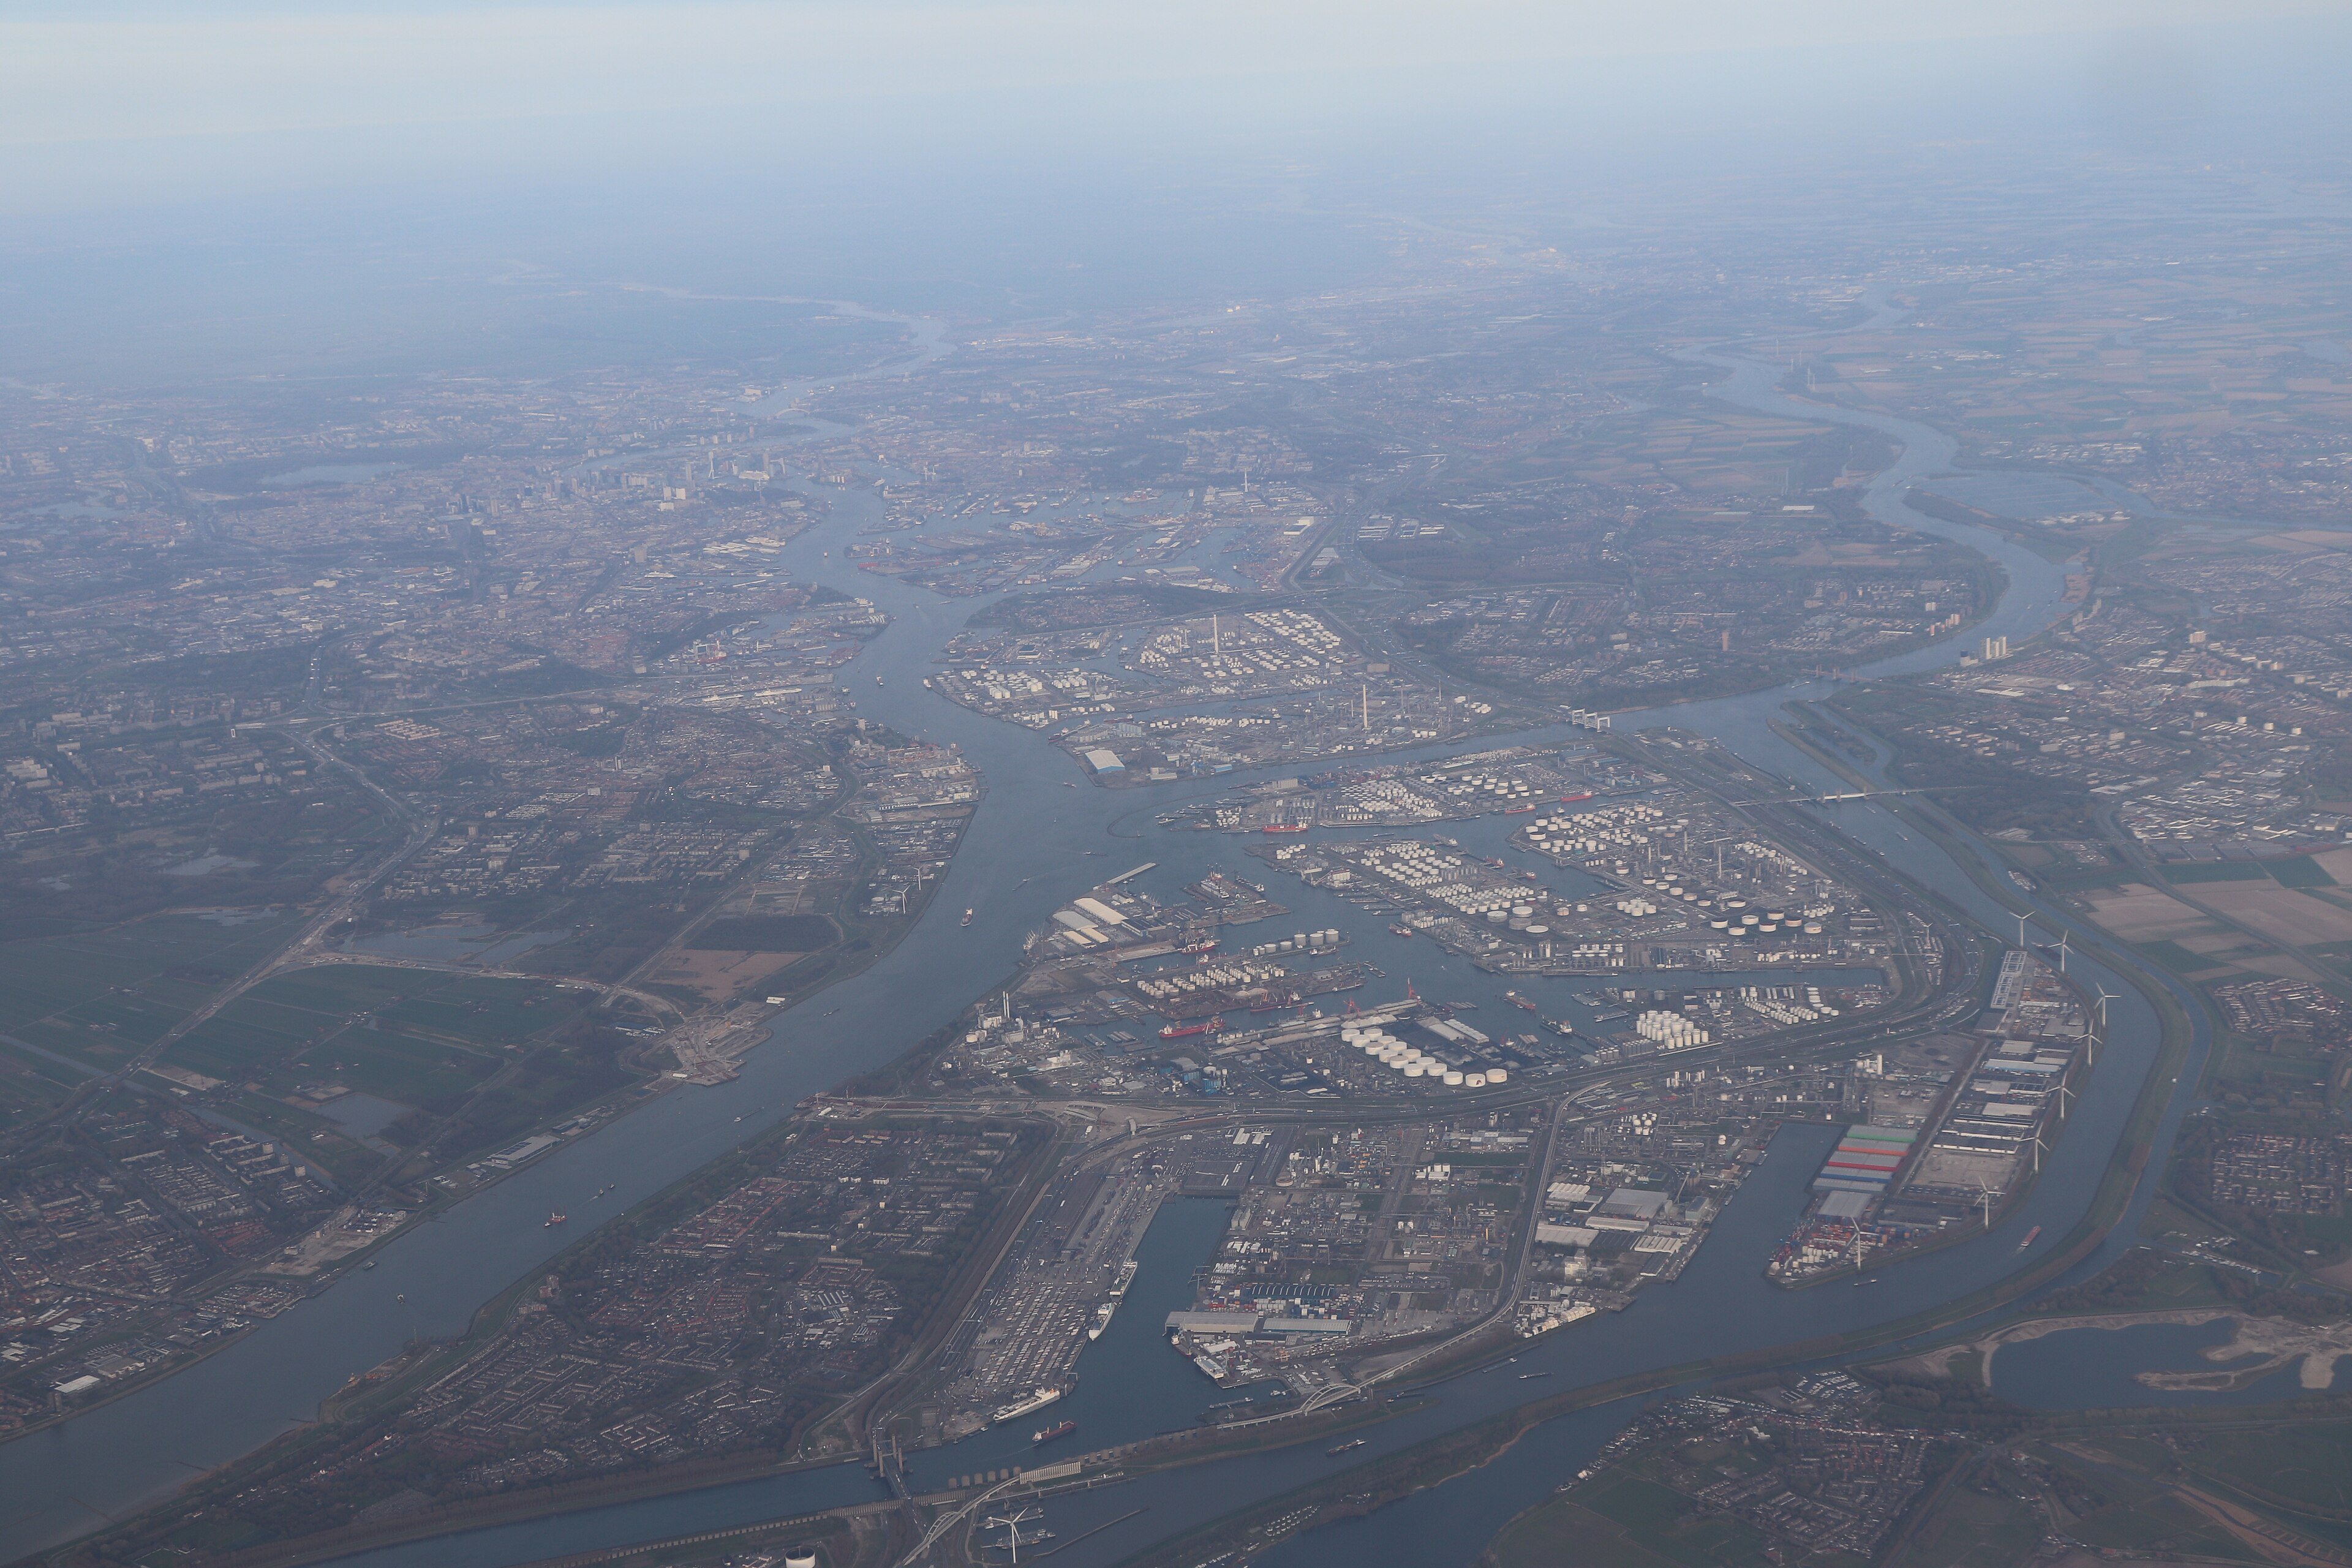
Photo: Andrzej Otrębski / Wikimedia Commons, CC BY-SA 4.0
- Two PHP flaws pushed governments, Wikipedia and Europe's biggest port offline
- A popular AI tool shipped a password stealer for about two hours
- A master key meant to be about 116 digits long was the number 4
New to this? A flaw in the code behind most websites forced governments and Wikipedia offline
On Wednesday 21 October 2026, the internet had one of its worst days on record. Governments switched off their own websites, a popular AI tool was turned into a password thief, and a cloud company froze every customer at once.
One post online listed the whole day's damage in a single paragraph with no full stops to breathe. It passed 3 million views within a day, and some readers begged the writer to use paragraphs. We checked each item on that list against official statements and security reports. This is what holds up.
Why did so many websites switch themselves off on Wednesday?
PHP is the free code that builds about 7 out of every 10 websites, including every WordPress site. On 21 October its makers released fixes for two flaws, now called PHP2Shell. Both let a stranger take over a web server without a password. Each was rated 9.2 out of 10 for danger.
The warnings that followed were blunt. The US National Security Agency told organisations to take the system offline "until it can be fully mitigated" if they could not update at once. The FBI's cyber division gave the same advice and asked anyone who had been hit to report it. So did British and European Union cyber agencies.
So the switch-off began. The Dutch national cyber agency pulled its own website. The Port of Rotterdam and the government portal Overheid.nl followed. Finland's state IT centre, Valtori, shut the government's public web services as "a precautionary measure". Denmark, France and Germany pulled sites too. Parts of Wikipedia, Archive.org and the forum Something Awful went dark, and the tech site How-To Geek reported outages at Asana and GOG.
The post says the bug details leaked before the fix was out, and that Censys counted about 1.5 million servers still on unfixed versions. Neither figure appears in an official statement. Our plain guide to the PHP flaw has the fixed version numbers and a WordPress checklist.
Did Japan's Prime Minister really tell people to take sites offline?
Yes. Prime Minister Sanae Takaichi asked website operators to check whether they ran PHP, get ready for the fix, and take sites offline for a while if they could not patch quickly. She called it an urgent request.
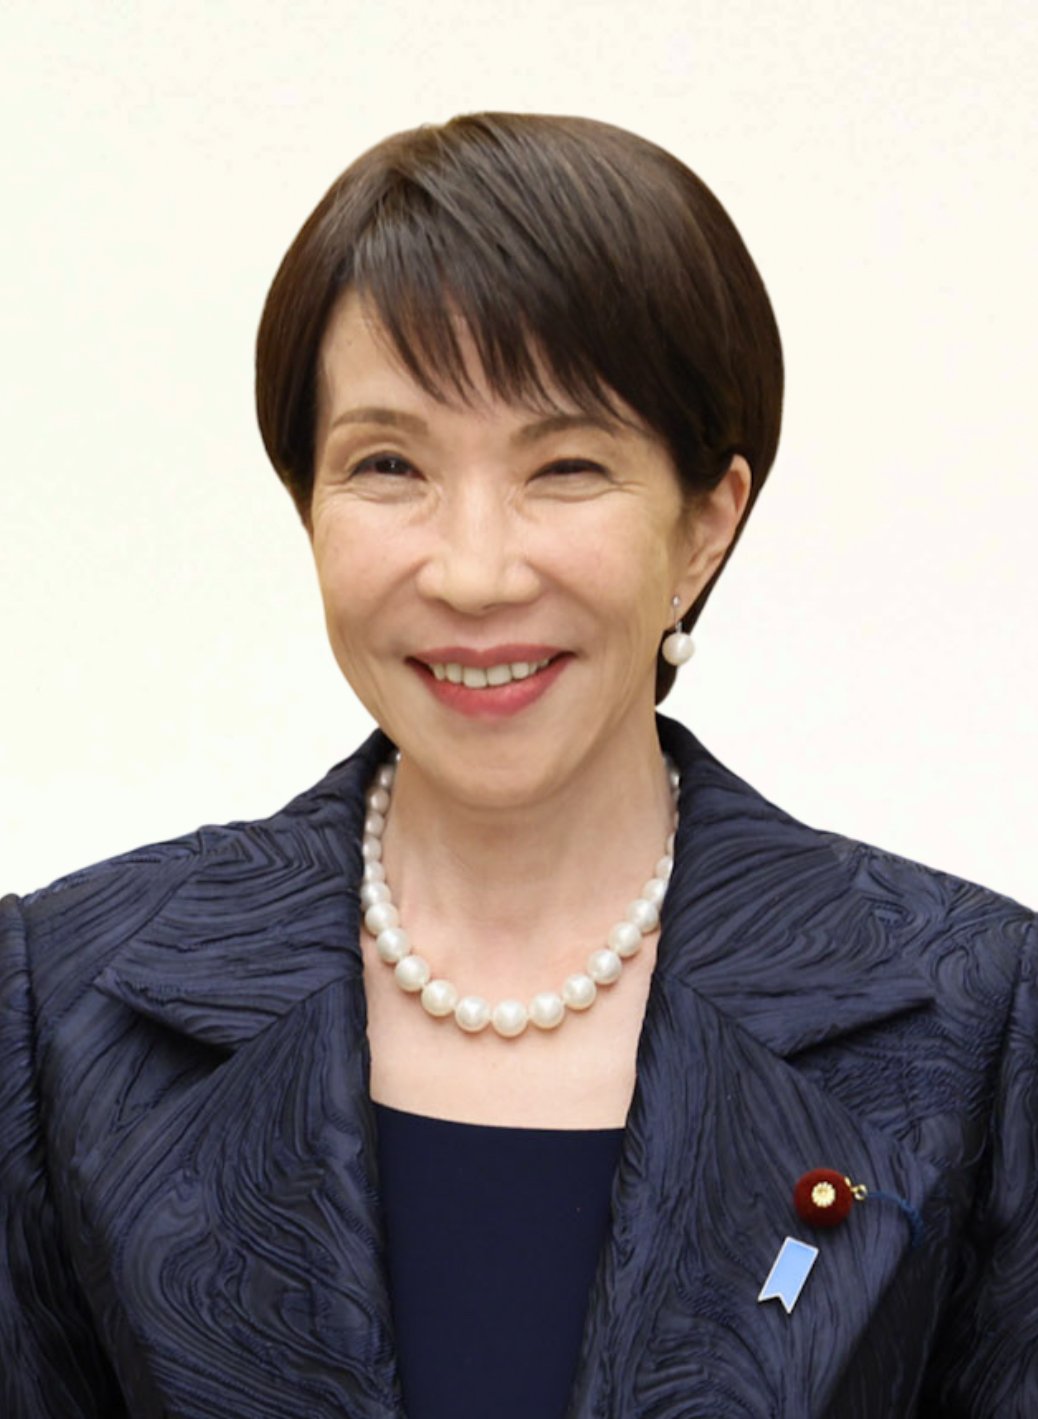
Photo: 首相官邸 (Cabinet Public Affairs Office) / Wikimedia Commons, CC BY 4.0
Japan listened. Mizuho's bank and securities arms halted services, Bloomberg reported. All Nippon Airways switched off its digital boarding passes. Japan Airlines, East Japan Railway and Seven-Eleven Japan took some web services down. Chief Cabinet Secretary Minoru Kihara said no attacks using the flaws had been confirmed. Cloudflare counted millions of attempts, but German, Dutch and Japanese officials say none has worked yet.
What broke on 21 October, and who has to act?
PHP was only the start. Here is every item from that day's list that official statements or two or more security reports back up, in date order.
| When | What broke | Who it hits | What to do |
|---|---|---|---|
| 1 to 5 Oct | Over 300 Tor exit relays hijacked to steal SSH passwords | People logging into servers over Tor | Change any password typed over Tor that week |
| 9 Sep to 7 Oct | Intruder inside TiDB Cloud with stolen logins | PingCAP's TiDB Cloud customers | Replace management API keys |
| 12 Oct | GitLab flaw rated 10 out of 10, exploit code now public | Firms running their own GitLab | Update GitLab |
| 14 to 17 Oct | Zeabur breached a second time, then announces closure | Zeabur customers | Move off before 31 December |
| 18 to 20 Oct | Eight eMudhra security keys found to be guessable | Anyone using a web browser | Keep your browser updated |
| 21 Oct | PHP2Shell fixes released, sites worldwide go offline | About 7 in 10 websites | Hosts must update PHP |
| 21 Oct | LiteLLM 1.107.0 ships a password stealer | Developers using AI tools | Treat the machine as hacked |
| 21 Oct | Railway pauses all deployments | Railway customers | Revoke and replace every secret |
| 21 Oct | Node.js fixes 10 flaws, one allowing code to run | Apps built on Node.js | Update and restart |
| 21 Oct | State Bank of India files a data loss | SBI customers | Watch for scam calls |
How did a popular AI tool end up stealing passwords?
LiteLLM is free software that programmers use to connect their apps to AI chatbots such as ChatGPT and Claude. On 21 October, someone published a poisoned version, 1.107.0. It held a program that grabs saved passwords and keys, plus a hidden remote control that lets the attacker run any code they like.
 Read nextNovember petrol forecast: Now about R3.01 more a litre
The bad copies sat on the main download site for about two hours, from 11:39 to 13:23 UTC. The official Docker images carried the same payload, including the one labelled "latest", until 14:20 UTC. LiteLLM says its release system was opened with stolen login tokens from a developer.
Its advice is stark. If you installed that version or started that image in those hours, assume the computer is compromised. It is the second time this year. In March, versions 1.82.7 and 1.82.8 were poisoned in the same way.
Why are developers being told to change every secret key?
Because three cloud companies lost control of customer secrets in a single month.
Railway, a service that runs other companies' apps, said on 21 October that someone got into the systems storing customers' environment variables. Those are the saved passwords and keys that let an app reach its database or payment provider. Railway paused every deployment on its platform and urged all users to revoke their keys.
PingCAP, which runs TiDB Cloud, says an intruder used stolen service logins inside its systems from 9 September to 7 October. A gang called FulcrumSec says it took 10.6 terabytes of data. PingCAP has not confirmed that number.
Zeabur, a Taiwanese hosting start-up, was breached on 14 October, its second break-in since late August. Three days later founder Yuanlin Lin announced the company will close. All its servers shut down by 31 December.
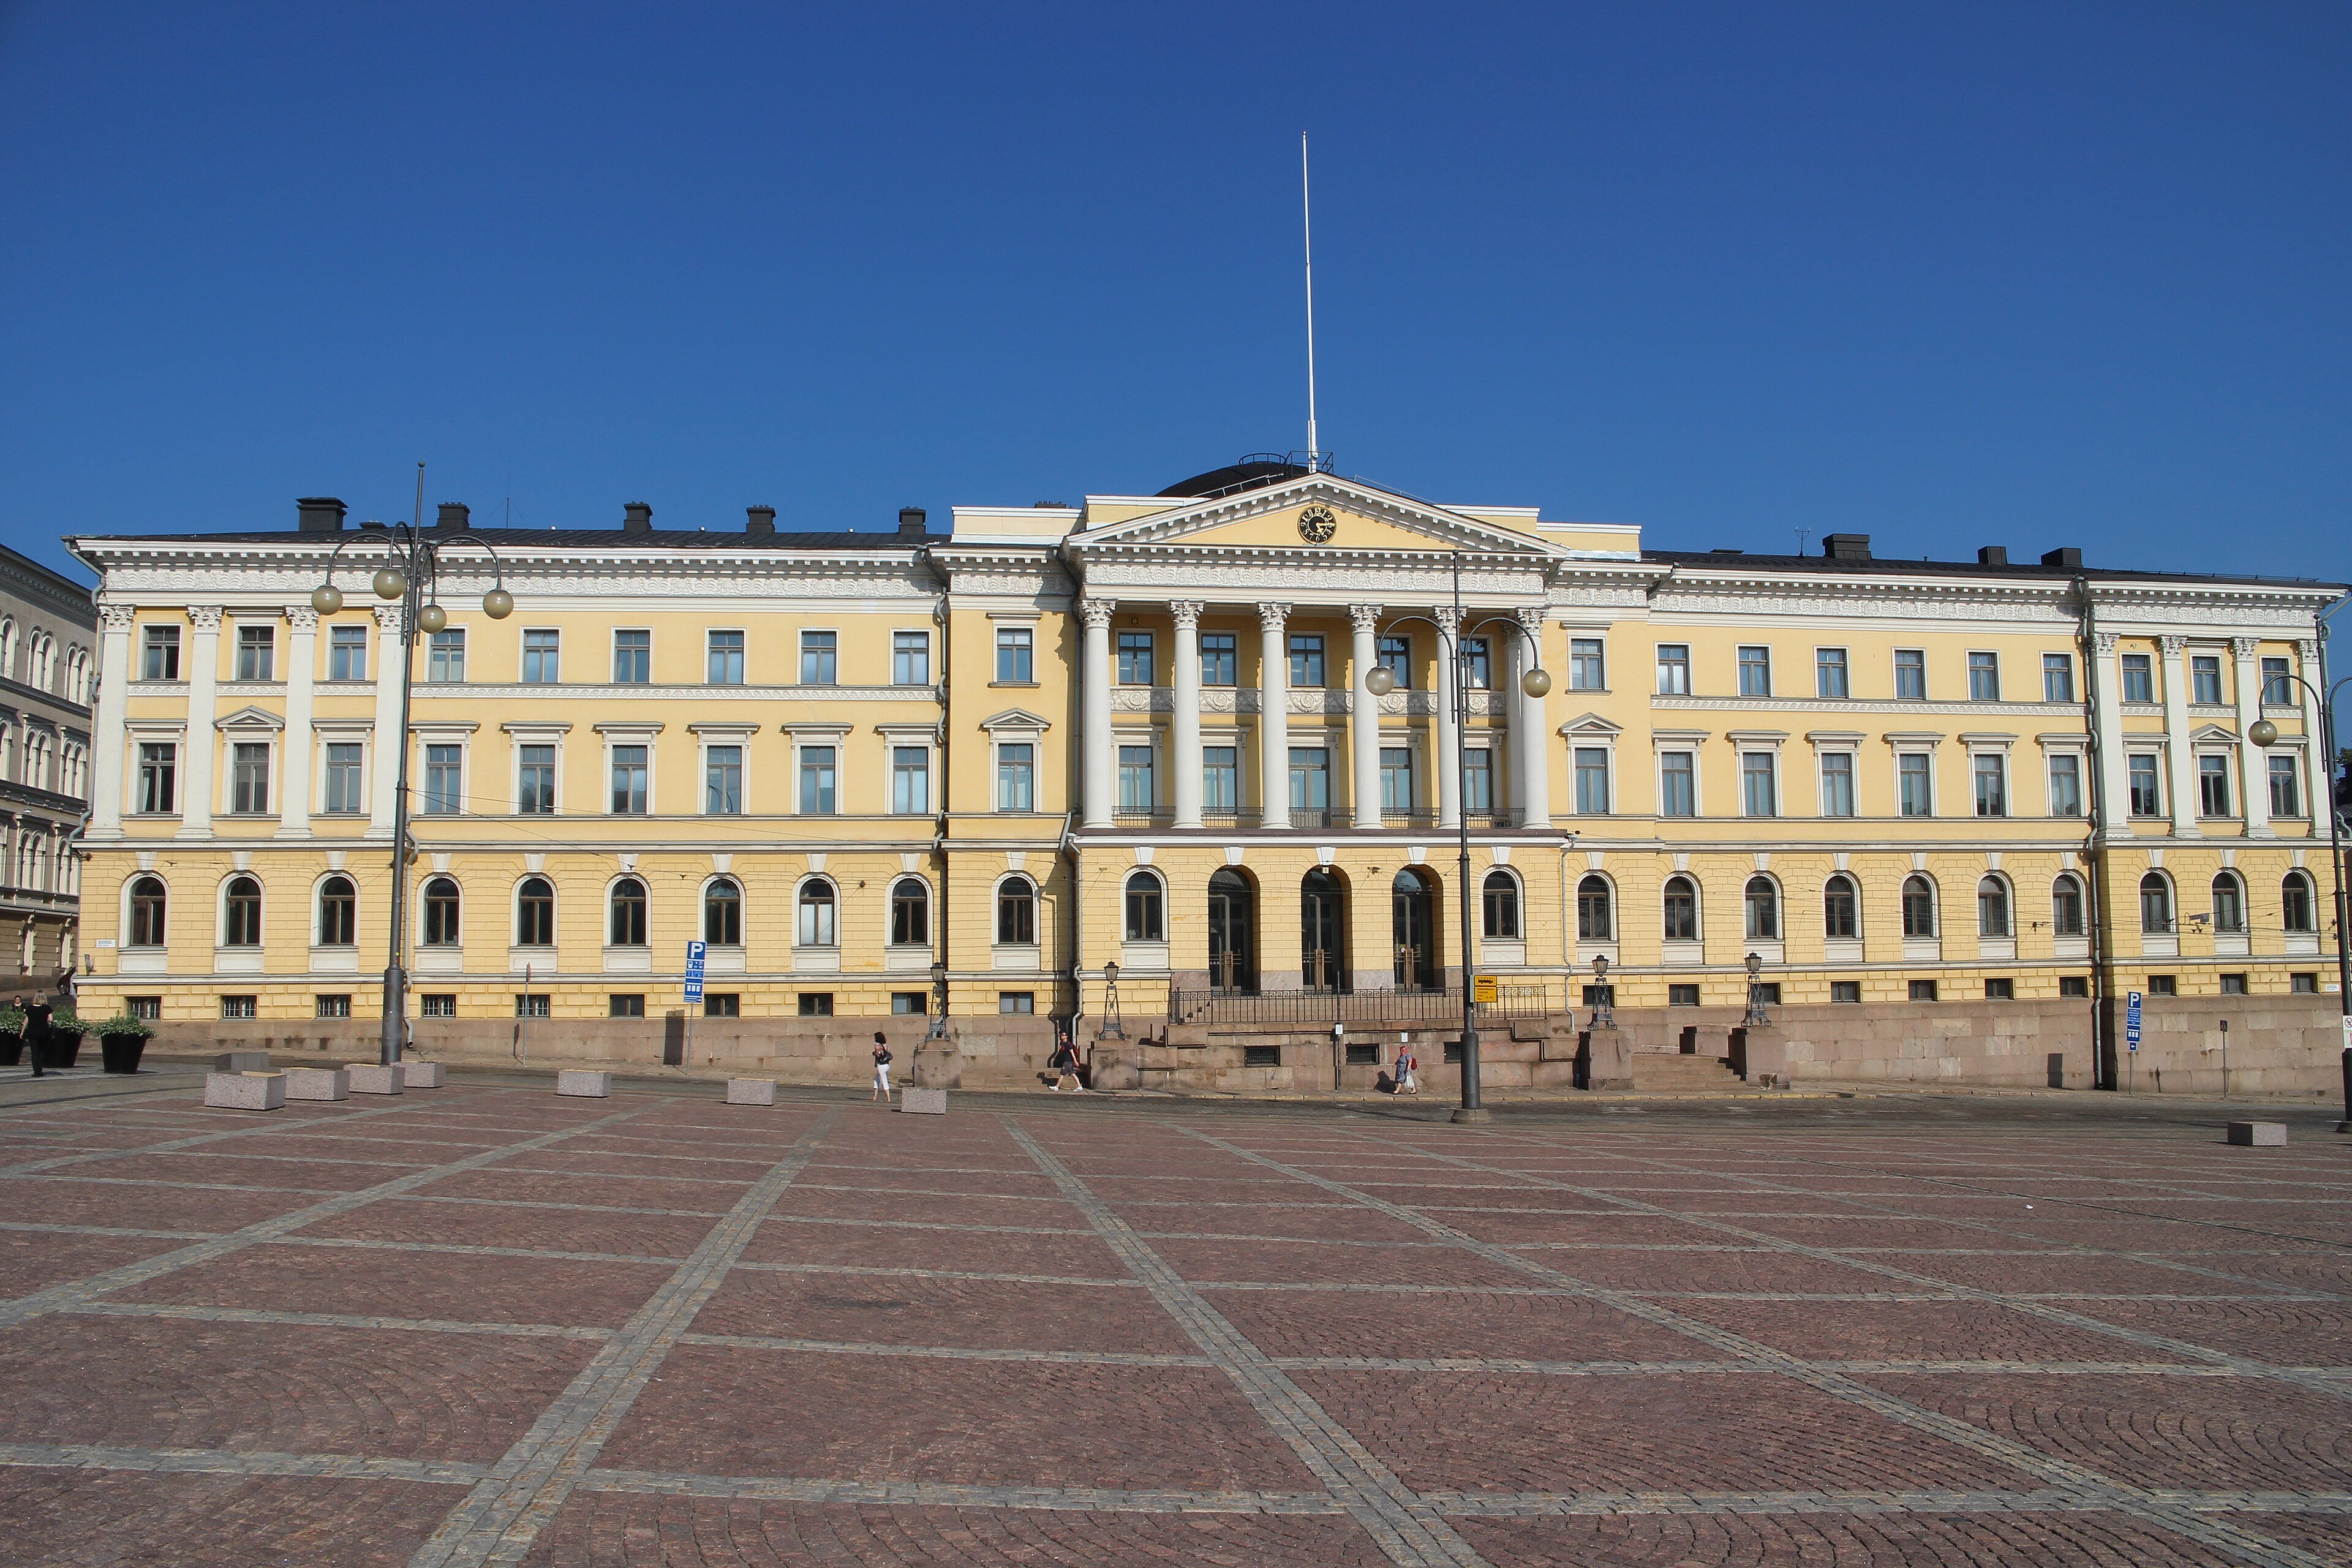
Photo: Suicasmo / Wikimedia Commons, CC BY-SA 4.0
Is Japan really in a state of emergency over cyber attacks?
Not officially. On 9 October Masaaki Taira, a former digital minister who heads the ruling party's cyber security team, said the situation could be called a state of emergency in cyberspace. The government itself has not declared one. More than 20 major Japanese firms, including JR East, have reported attacks in recent weeks.
 Trending nowScammers already know your account details before they call, and that is what makes them so convincing
India had its own shock. On 21 October, State Bank of India told the stock exchange it had "experienced an incident involving the loss of certain data". It found 3,897 records with customers' names, phone numbers and addresses. If you bank in South Africa, the same rule applies. A call about a "security incident" is the moment scammers love, as Standard Bank customers caught in OTP fraud found out.
What should ordinary people do after a day like this?
Most of this hits companies, not your laptop. A few simple steps still help.
- Update your phone, computer and web browser today. Chrome, Firefox, Safari and Edge have already blocked the bad eMudhra certificates.
- If you use the same password on several sites, change your email and banking passwords first.
- If you run a small WordPress site, ask your web host whether PHP is on 8.5.12, 8.4.27, 8.3.36 or 8.2.35.
- Treat any email or call about "urgent security updates" with suspicion. Real banks never ask for your PIN or OTP.
Follow every new turn on our PHP flaw page.
How can a master key be the number 4?
eMudhra is an Indian certificate authority. Its whole job is to vouch that a website is really who it says it is. That vouching is what puts the small padlock next to a web address.
Photo: Santeri Viinamäki / Wikimedia Commons, CC BY-SA 4.0
Each of its vouching certificates is protected by a private key, a secret number. For this kind of key, the number should be about 116 digits long. Guessing it should take longer than the age of the universe.
The Register and The Hacker News reported that eight of eMudhra's keys, made in April 2025, were all smaller than 256. Anyone could crack them by trying 256 numbers. The post claims others were 66 and 237, and that eMudhra has issued over 60 million certificates.
eMudhra says a step in its key-making ceremony created a weak second set of keys, and those were the ones sent to the browsers. It says it has no evidence anyone misused them. Chrome and Firefox blocked them within hours. Apple and Microsoft followed. Google will drop the whole root from Chrome on 27 October.
The key that was meant to guard the padlock for "EM OV TLS CA - G3C" was a number you could count on one hand. It was 4.
Get the stories that hit your pocket
Petrol, SARS, Eskom, grants and the news everyone is talking about. One short email every weekday at 6am.
Free. One email each weekday. Unsubscribe anytime.Sources23
- Original post, 21 Oct 2026
- FBI Cyber Division warning on CVE-2026-109618 and CVE-2026-109619 (21 Oct 2026)
- India TV News, NSA warns of PHP flaw, advises taking unpatched servers offline
- CNN, AI finds cybersecurity issue affecting 70% of the internet
- heise, PHP2Shell updates roll out as websites go offline
- UptimeRobot, inside PHP2Shell: why websites took themselves offline
- How-To Geek, your favorite websites are down
- The Next Web, millions of PHP2Shell attempts but no confirmed break-in
- Japan Cyber Watch, Japan takes websites offline with the Prime Minister's backing
- CSA Singapore, critical vulnerability in GitLab CE and EE
- LiteLLM, security incident: release v1.107.0 compromised (21 Oct 2026)
- Datadog Security Labs, LiteLLM supply chain compromise
- Sonatype, the March 2026 LiteLLM compromise
- TechCrunch, Railway urges all users to revoke secret keys (22 Oct 2026)
- PingCAP, TiDB Cloud security update, October 2026
- Zeabur, Zeabur is shutting down
- Node.js, 21 October 2026 security releases
- The Hacker News, attackers hijacked over 300 Tor exit relays
- The Hacker News, State Bank of India confirms data leak
- The Next Web, Japan steps up cyber warnings as data leaks hit millions
- The Register, eMudhra's private keys compromised, one was the number 4 (20 Oct 2026)
- The Hacker News, eight eMudhra CA keys compromised
- eMudhra, statement on recent certificate security incident
Keep reading
 ExplainedA flaw in the code behind most websites forced governments and Wikipedia offline
 ExplainedHow often MS misdiagnosis really happens, and how doctors catch it
 ExplainedThe interest on a $300,000 home loan now costs more than the loan